By Carl Ballenger, CISSP, CCSP | Published on CarlsCloud™
Subscribe Free to the CarlsCloud™ Newsletter: Get weekly deep dives into real-world zero-day tradecraft, federal compliance baselines (NIST SP 800-53/800-63), and scenario-based CISSP & CCSP exam dissections.
In our recent analysis of Warp Panda's zero-day exploitation of VMware ESXi (CVE-2026-41709), we broke down how a China-nexus cyber espionage group weaponized an insufficient logging flaw carrying a CVSS score of just 2.7 to blind host audit trails during lateral movement.
That real-world intrusion highlights one of the most critical operational dilemmas facing security leaders today: What happens when your organization's formal policy says a vulnerability is Low priority, but threat intelligence confirms an adversary is actively exploiting it against your sector?
This exact tension—between rigid policy compliance and threat-informed risk management—is a favorite proving ground on both the ISC2 CISSP and CCSP exams. Questions built around these scenarios are designed to filter out candidates who rely purely on rigid metric thresholds from those who possess the strategic "Think Like a Manager / Cloud Architect" mindset.
Below is a scenario-based practice question inspired by the ESXi campaign, followed by an in-depth breakdown of the testable exam domains and the cognitive traps built into each distractor.
Scenario-Based CISSP / CCSP Practice Challenge
Test your decision-making against this realistic enterprise scenario:
Scenario: An enterprise security operations center (SOC) receives a threat intelligence advisory confirming that an advanced persistent threat (APT) targeting its industry is actively chaining an edge appliance exploit with a newly disclosed hypervisor logging vulnerability (CVSS base score: 2.7).
The hypervisor flaw allows attackers who have already obtained administrative privileges to execute host-level commands without generating syslog events.
Under the organization's existing vulnerability management standard, vulnerabilities with a CVSS score below 4.0 are scheduled for remediation during the next quarterly maintenance window.
What should the Information Security Manager recommend FIRST?
A. Immediately shut down all hypervisor hosts until the vendor patch can be validated in a staging environment.
B. Reassess the risk rating using contextual threat intelligence, initiate emergency change management to apply the patch, and deploy compensating network-level monitoring.
C. Adhere to the established vulnerability management policy and defer patching until the quarterly maintenance window since the CVSS score is Low (2.7).
D. Reconfigure the SIEM to increase the retention period of existing hypervisor syslogs from 90 days to 365 days.
The Correct Answer is B.
To see why B is the only defensible management response—and why options A, C, and D are classic ISC2 trap answers—let's deconstruct the underlying domains.
Deconstructing the Exam Domains: CISSP & CCSP Mappings
CISSP Domain 1.9 & CCSP Domain 6: The Fallacy of CVSS == Risk
One of the most dangerous operational traps in security management is treating the Common Vulnerability Scoring System (CVSS) base score as an absolute proxy for organizational risk.
On the CISSP Exam, risk is governed by a fundamental formula:
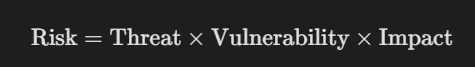
Vulnerability: CVSS base metrics measure intrinsic technical severity in a vacuum (attack vector, privileges required, user interaction, scope). A base score of 2.7 accurately reflects that CVE-2026-41709 requires prior administrative privileges and does not directly crash the host or grant unauthenticated remote code execution.
Threat: Static CVSS base scores completely omit threat actor capability and intent. When intelligence confirms that an espionage group like Warp Panda is actively weaponizing the flaw in production networks, or when CISA adds the flaw to the Known Exploited Vulnerabilities (KEV) catalog, the Threat Likelihood moves from theoretical to imminent.
Impact: While the loss of local host log lines might seem minor in isolation, in a post-exploitation kill chain it directly destroys Nonrepudiation and Accountability (CISSP Domain 1.2). The SOC loses the forensic telemetry needed to determine scope, identify lateral movement, and contain a breach.
Exam Mindset Callout (The Strategic Risk Advisor): On the exam, security managers do not blindly outsource decisions to a third-party score feed. They contextualize technical metrics with active threat intelligence, business impact, and asset criticality to calculate true Organizational Risk.
2. CISSP Domain 7.8, 7.9 & CCSP Domain 5: Emergency Change Management vs. Policy Dogmatism
Policies and standards provide baseline operational consistency. However, mature governance frameworks (CISSP Domain 1.3) explicitly mandate policy exception procedures and emergency change advisory boards (ECAB).
When a low-severity flaw is actively targeted by an APT in the wild, adhering strictly to a calendar-based patching cycle without formal review is not governance—it is negligence. The Information Security Manager's duty of Due Care requires:
Reassessing Risk: Documenting that confirmed in-the-wild exploitation overrides the default CVSS tiering.
Invoking Emergency Change Management (CISSP Domain 7.9): Expediting patch testing and rollout rather than waiting 90 days for the next scheduled maintenance window.
Deploying Compensating Controls (CISSP Domain 3.1 & CCSP Domain 5): Because enterprise hypervisor patching takes time, the manager immediately layers defense-in-depth measures—such as east-west Network Detection and Response (NDR), hypervisor configuration drift alerting, and micro-segmentation—to detect adversary presence while the patch is validated.
Anatomy of the Distractors: Why the Other Options Fail
ISC2 questions are crafted to exploit specific cognitive biases. Here is why each incorrect option falls apart under scrutiny:
Option A: The "Technical Knee-Jerk" (Immediately Shut Down All Hypervisors)
The Trap: It eliminates technical risk immediately. Tactical administrators under pressure often default to drastic containment.
Why It Fails: In CISSP Domain 1.3 and CCSP Domain 1, security must support the organization's business mission and continuity. Shutting down hypervisor clusters induces a self-inflicted Denial of Service (DoS), crashing tenant virtual machines, business-critical databases, and enterprise revenues. Furthermore, technical managers cannot unilaterally take business-stopping actions without explicit authorization from senior risk executives.
Option C: The "Policy Dogmatist" (Defer Patching Until Quarterly Maintenance)
The Trap: It adheres to written company policy to the letter. Compliance-first mindsets lean here because "following policy avoids blame."
Why It Fails: Written standards are operational baselines, not suicide pacts. Failing to act when verified intelligence warns of active adversary exploitation breaches both the Due Diligence and Due Care legal standards tested in CISSP Domain 1.3. Blindly waiting months while an APT operates unlogged in your hypervisors is always an exam trap.
Option D: The "Illusion of Action" (Increase SIEM Log Retention to 365 Days)
The Trap: It sounds proactive and cites a valid security concept (log retention compliance under NIST SP 800-53 AU-11).
Why It Fails: This option suffers from a fatal logical flaw: you cannot retain logs that were never recorded in the first place. Because CVE-2026-41709 suppresses the generation of audit records at the hypervisor daemon level, extending SIEM storage retention merely retains empty logs for longer. It does nothing to detect the intrusion or fix the defect.
The Enterprise Takeaway: Modernizing Your Vulnerability Management Playbook
If your enterprise still runs vulnerability management solely on "CVSS > 7.0 = Patch, CVSS < 4.0 = Defer", here are three architectural modernizations to implement:
| Traditional Metric-Driven Vulnerability Management | Threat-Informed Contextual Risk Management |
|---|---|
| Remediation priority dictated solely by static CVSS Base v3.1/v4.0 scores. | Remediation priority dynamically weighted by CVSS + Exploit Prediction Scoring System (EPSS) + CISA KEV presence + Threat Intel feeds. |
| Strict adherence to quarterly patch windows for any vulnerability rated Low/Medium. | Automated exception triggering: Confirmed active in-the-wild exploitation automatically escalates remediation to Emergency/Out-of-Band status. |
| Reliance on host-level syslog agents as the sole source of truth for administrative actions. | Multi-layered observability: Correlating host syslogs with out-of-band network flow logs (VPC flow logs, NDR) and hardware root-of-trust attestation (TPM). |
Join the Conversation on CarlsCloud™
How does your organization handle policy exceptions when threat intelligence contradicts a low CVSS score? Have you automated KEV-based escalation in your vulnerability pipelines?
Subscribe Free to the CarlsCloud™ Newsletter: Get weekly deep dives into real-world zero-day tradecraft, federal compliance baselines (NIST SP 800-53/800-63), and scenario-based CISSP & CCSP exam dissections.
Level Up Your Certification Prep: Check out our dedicated CarlsCloud™ CISSP Prep Resources for curated question breakdowns, memory aids, and architectural strategy guides tailored for cloud and infrastructure leaders.
Did you enjoy CarlsCloud.com™ today and did I help you at all?
If so, buy me a coffee or just shoot me a note via LinkedIn to say thanks it would mean a lot! -Carl