VMware
VMware is a virtualization and cloud computing software vendor based in Palo Alto, California. Founded in 1998, VMware is now a subsidiary of Dell Technologies. VMware bases its virtualization technologies on its bare-metal hypervisor ESX/ESXi in x86 architecture.
When a "Low-Severity" 2.7 CVSS Score Becomes a Zero-Day Weapon: Inside the Warp Panda VMware ESXi Logging Exploit (CVE-2026-41709)
Real-world nation-state tradecraft rarely stays inside a single technical silo. If you are preparing for or maintaining your CISSP or CCSP, the Warp Panda campaign connects directly to several high-weight exam objectives...
CISA: VMware Releases Critical Security Updates for VMware vRealize Log Insight
VMware released security updates to address multiple vulnerabilities in VMware vRealize Log Insight. A remote attacker could exploit these vulnerabilities to take control of an affected system...
New Python malware backdoors VMware ESXi servers for remote access
The new python backdoor adds seven lines inside "/etc/rc.local.d/local.sh," one of the few ESXi files that survive between reboots and is executed at startup.
VMware Beware: Lockbit 3.0 Targeting ESXi hash: 0f7c10dfa562adf15f1f6078ecaee788
Per Twitter @Unit42_Intel a LockBit 3.0 variant using ESXi Locker version 1.2 continues targeting ESXi hash: 0f7c10dfa562adf15f1f6078ecaee788.
ESXi Alert: Bad VIB(E)s Part Two: Detection and Hardening within ESXi Hypervisors
In part one, we covered attackers’ usage of malicious vSphere Installation Bundles (“VIBs”) to install multiple backdoors across ESXi hypervisors, focusing on the malware present within the VIB payloads. In
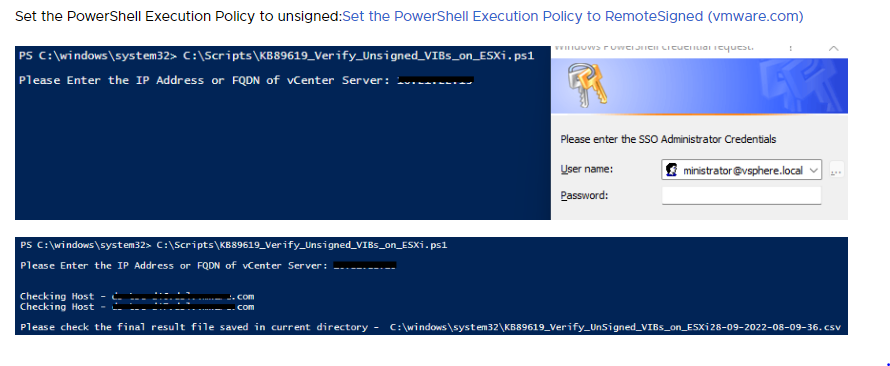
HOWTO: KB89619 – Mitigation and Threat Hunting Guidance for Unsigned vSphere Installation Bundles (VIBs) in ESXi (89619)
On Thursday September 29th, Mandiant published information on malware they discovered in the wild that leverages unsigned VIBs to install backdoors on a compromised ESXi host.
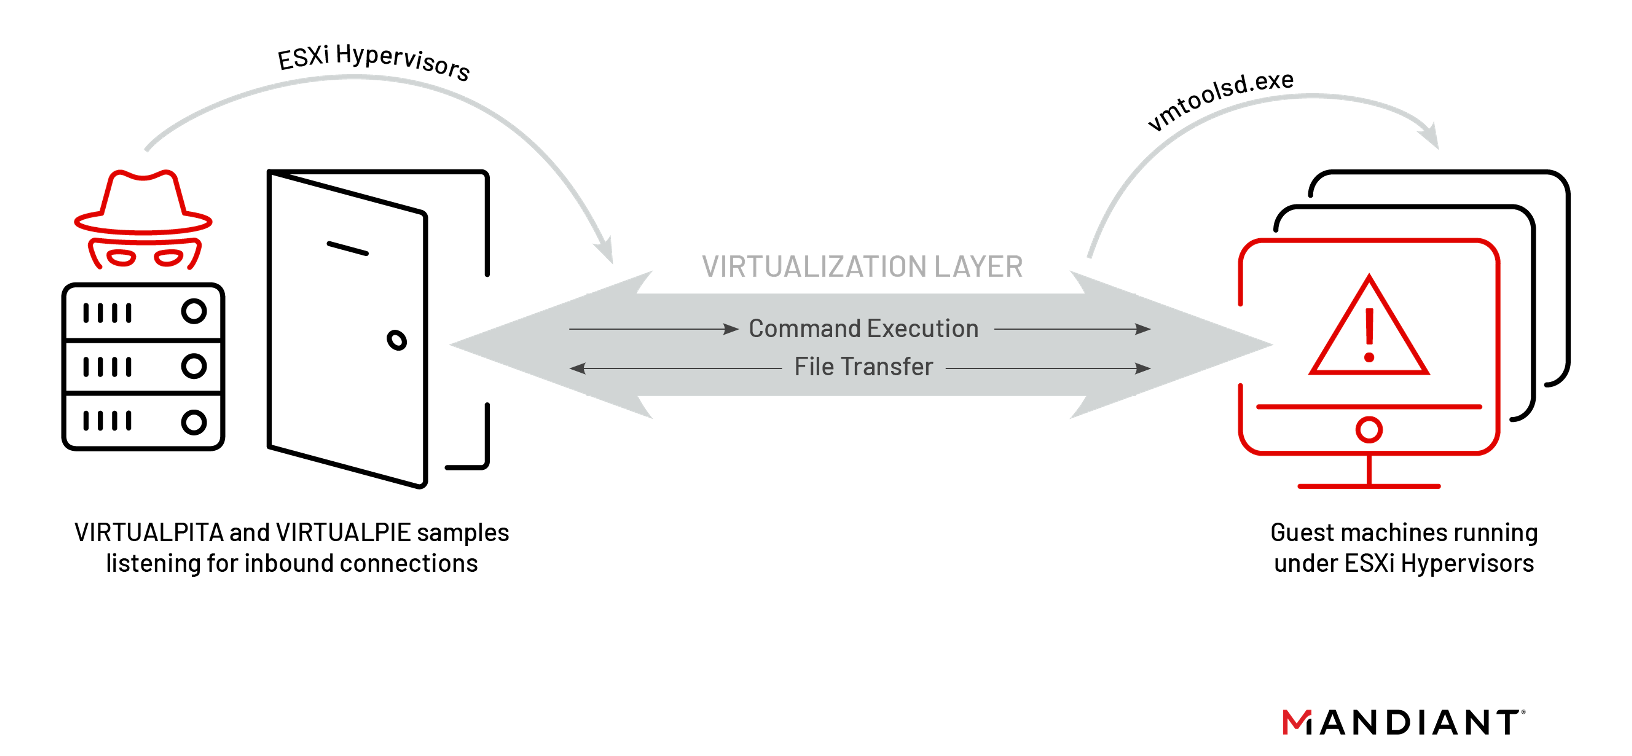
ESXi ALERT: Bad VIB(E)s Part One: Investigating Novel Malware Persistence Within ESXi Hypervisors
This malware ecosystem was initially detected during an intrusion investigation when Mandiant identified attacker commands sourced from the legitimate VMware Tools process, vmtoolsd.exe, on a Windows virtual machine hosted on a VMware ESXi hypervisor.