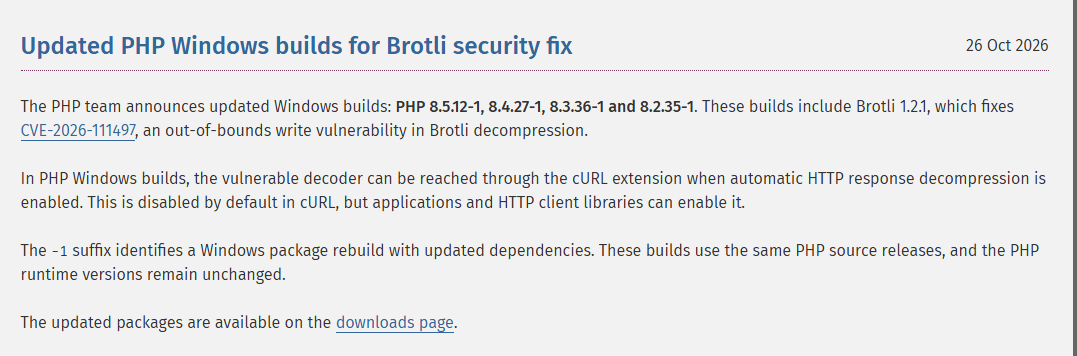
10-26-26 - UPDATE: 2nd PHP Windows Security Update in Five Days to Fix Brotli Code Execution Flaw
Hacker News Articles and Resources
10-26-26 - UPDATE: 2nd PHP Windows Security Update in Five Days to Fix Brotli Code Execution Flaw
In late September, ShinyHunters hacked the FBI recruitment website fbijobs.gov and taunted the agency by threatening to publish...
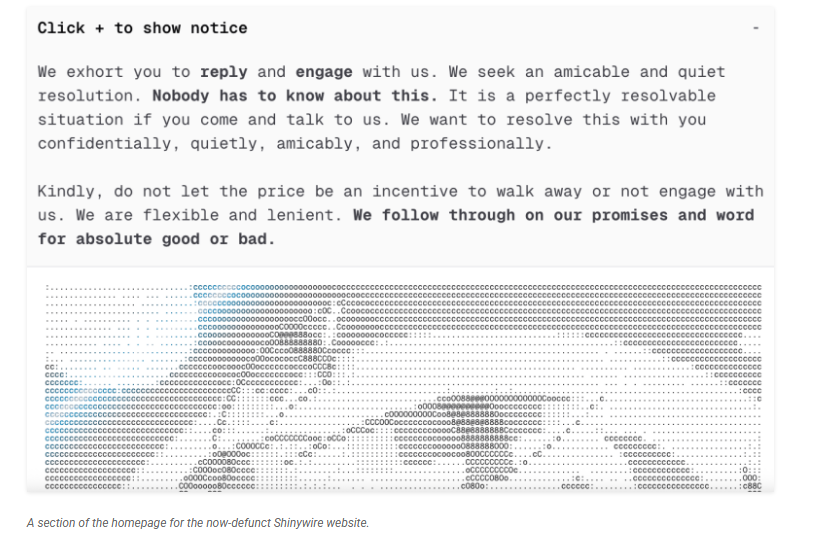
The Seizure Operation Visitors to the RAMP dark web and clearnet domains are now greeted with a stark seizure notice.
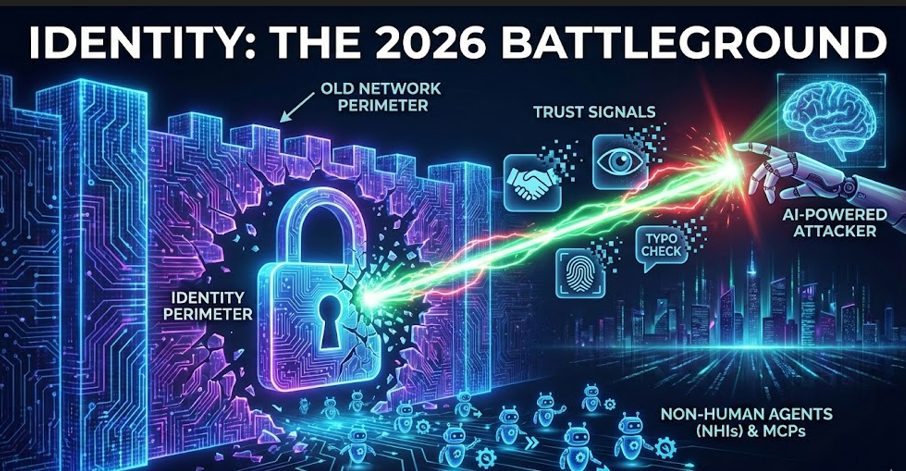
The consensus for 2026 is clear: Identity is the battlefield, but the rules of engagement have changed.
Communication services provider Twilio this week disclosed that it experienced another "brief security incident" in June 2022 perpetrated by the same threat actor behind the August hack that resulted in unauthorized access of customer information.
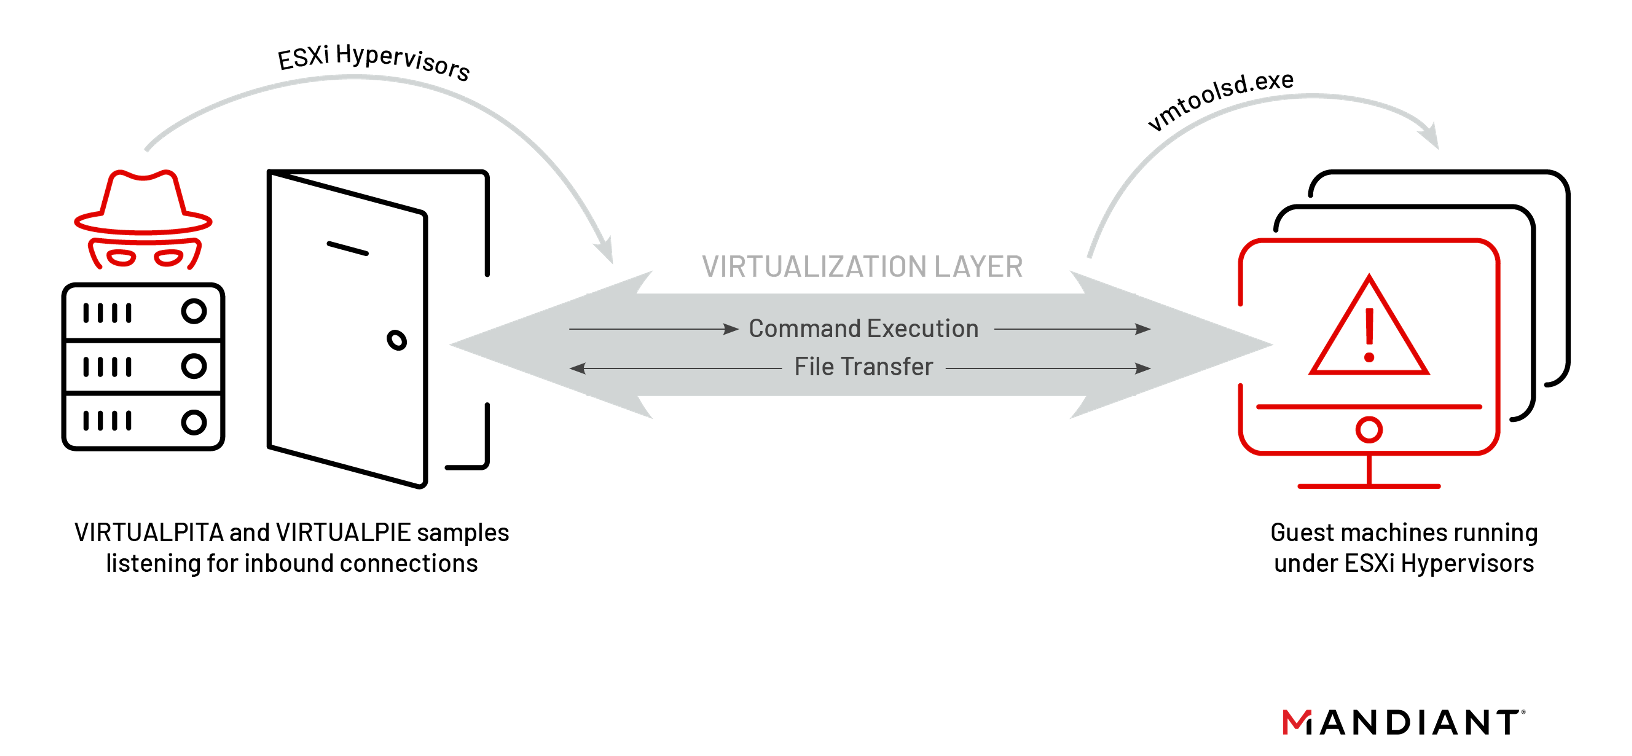
This malware ecosystem was initially detected during an intrusion investigation when Mandiant identified attacker commands sourced from the legitimate VMware Tools process, vmtoolsd.exe, on a Windows virtual machine hosted on a VMware ESXi hypervisor.
The reward offer, first reported by WIRED, is also notable for the fact that it marks the first time the face of a Conti associate, known as "Target," has been unmasked. The four other associates have been referred to as "Tramp," "Dandis," "Professor," and "Reshaev."