VMware Beware: Lockbit 3.0 Targeting ESXi hash: 0f7c10dfa562adf15f1f6078ecaee788
Per Twitter @Unit42_Intel a LockBit 3.0 variant using ESXi Locker version 1.2 continues targeting ESXi hash: 0f7c10dfa562adf15f1f6078ecaee788.
Common Attack Vector Information and Related Articles
Per Twitter @Unit42_Intel a LockBit 3.0 variant using ESXi Locker version 1.2 continues targeting ESXi hash: 0f7c10dfa562adf15f1f6078ecaee788.
In part one, we covered attackers’ usage of malicious vSphere Installation Bundles (“VIBs”) to install multiple backdoors across ESXi hypervisors, focusing on the malware present within the VIB payloads. In
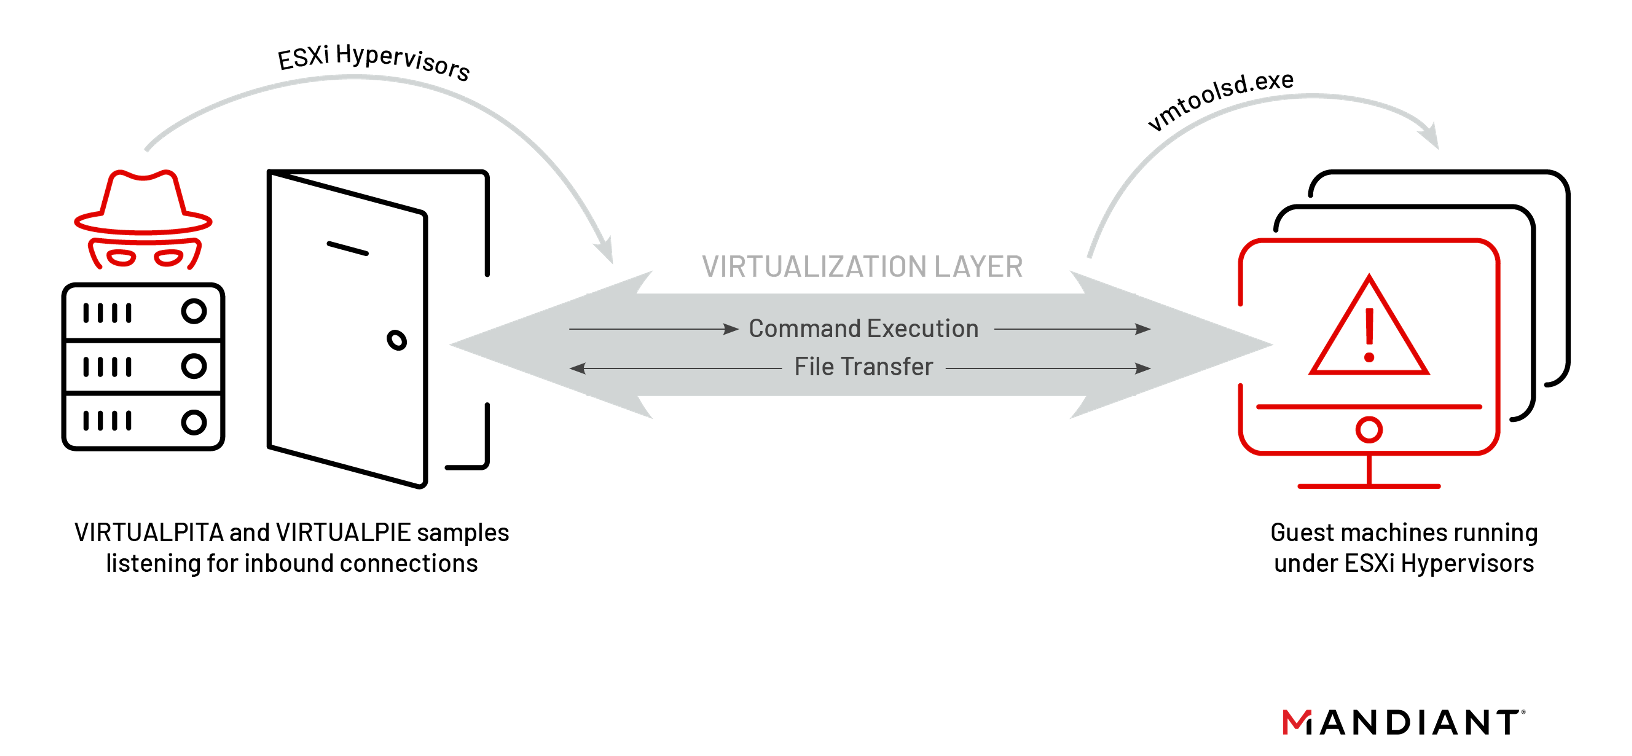
On Thursday September 29th, Mandiant published information on malware they discovered in the wild that leverages unsigned VIBs to install backdoors on a compromised ESXi host.
This malware ecosystem was initially detected during an intrusion investigation when Mandiant identified attacker commands sourced from the legitimate VMware Tools process, vmtoolsd.exe, on a Windows virtual machine hosted on a VMware ESXi hypervisor.
"Since December 2021, multiple threat actor groups have exploited Log4Shell on unpatched, public-facing VMware Horizon and [Unified Access Gateway] servers," the agencies said. "
A first-of-its-kind security analysis of iOS Find My function has identified a novel attack surface that makes it possible to tamper with the firmware and load malware onto a Bluetooth chip that's executed while an iPhone is "off."