By Carl Ballenger, CISSP, CCSP | CarlsCloud.com
So.... if your Security Operations Center (SOC) is still treating cloud resource hijacking strictly as a "cryptojacking" problem—watching for sustained CPU spikes from illicit Monero miners—your threat model is officially outdated. According to newly released threat intelligence from Google Threat Intelligence Group (GTIG) and Mandiant, cybercriminals have pivoted to a far more lucrative, high-velocity racket: LLMjacking.
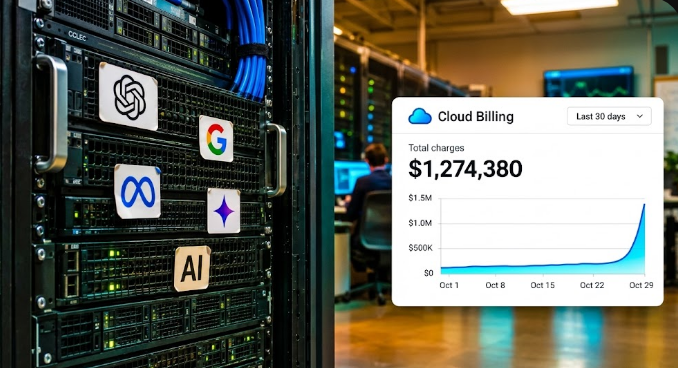
Instead of slowly burning compute cycles over weeks to mine cryptocurrency, threat actors are hijacking enterprise access to frontier Large Language Models (LLMs), routing underground traffic through stolen API keys, and leaving victim organizations on the hook for massive consumption bills.
Google observed individual incidents generating over $100,000 USD in fraudulent charges in a single day, with cumulative enterprise losses hitting $1 million USD before administrators managed to revoke access.
For cloud security architects, federal IT practitioners, and anyone preparing for the ISC2 CISSP or CCSP exams, LLMjacking is a masterclass in how non-human identity sprawl, API routing vulnerabilities, and shadow AI collide in production cloud environments.
The Technical Breakdown: Inside the LLMjacking Kill Chain
LLMjacking targets backend foundation models directly by compromising valid cloud identities or publicly exposed LLM endpoints. Rather than merely tricking a public customer-support chatbot into writing code, attackers go straight for the backend billing quota.
Initial Access & Credential Harvesting
Attackers are bypassing perimeter defenses by targeting non-human identities and developer tokens across North America, South America, and APAC:
Exposed Identity Tokens
Threat actors actively scrape public GitHub repositories, misconfigured environments, and client-side code for cloud IAM credentials, Service Account keys, GitHub Personal Access Tokens (PATs), and active session tokens.
UNC6993 & Session Hijacking
Google highlighted threat actor UNC6993, which breached a cloud instance using a misconfigured Service Account key to tap into an LLM API. UNC6993 also stood up a spoofed application portal inviting victims to "join a group of LLM users"—tricking users into copying and pasting their raw JSON payload (containing an active access token) from the legitimate LLM service straight into the attacker's backend API, completely bypassing password and MFA controls.
Privilege Escalation, Persistence & Lateral Movement
Once inside a cloud tenant, actors move rapidly to lock in persistence and evade rate limits:
Abusing Token-Creation Privileges
Attackers exploit service accounts with token-generation permissions to mint temporary credentials for high-privilege accounts, harvesting database passwords and third-party API keys from cloud secret managers.
Stealth Persistence
Threat actors inject SSH keys into compute instances and spin up rogue backdoor service accounts disguised as benign internal tools—such as "internal billing optimization utilities."
"Burn and Rotate" Evasion
To bypass provider rate limits, actors continuously script the creation and deletion of short-lived service accounts and API keys.
Middleware Exploitation
Attackers specifically target LLM routing infrastructure, exploiting flaws like CVE-2026-40217 in LiteLLM to escalate privileges and hijack model routing.
Monetization via "LLM Mixers" & Grey-Market Relays
The underground ecosystem has matured into a division of labor featuring LLM Mixers—illicit routing gateways that aggregate stolen enterprise API quotas and resell them via criminal storefronts:
Jet Night (jet-night[.]com)
An underground LLM Mixer offering "unlimited token plans" with access to frontier models for roughly $60/month, funded entirely by siphoning enterprise victim quotas.
Hijacked Developer CLIs (Symantec / Carbon Black Report)
Researchers uncovered a grey-market relay active across APAC (impacting manufacturing, semiconductor, petrochemical, and pharmaceutical sectors) that targets employees trying to bypass regional AI restrictions. After installing legitimate OpenAI Codex or Anthropic Claude Code CLIs via npm, users run a fileless PowerShell or bash script from a lookalike domain (vibe.aiok[.]me). This script rewrites ~/.codex/config.toml or ~/.claude/settings.json, disables telemetry, switches execution sandboxing completely off (danger-full-access in Codex), and routes every prompt and code block through third-party relay servers.
Through the CISSP and CCSP Lens: Testable Domain Breakdown
When we strip away the AI buzzwords, LLMjacking exposes fundamental failures in identity governance, software supply chain integrity, and cloud operations.
CISSP Domain 5: Identity &Access Management (IAM) (13%)
Domain Mapping
- Non-Human Identity (NHI) governance, Service Account lifecycle management, Just-In-Time (JIT) access, Policy Decision/Enforcement Points (PDP/PEP), and privilege escalation.
Real-World Connection
Nearly every LLMjacking breach starts with over-privileged, long-lived Service Account keys or PATs coupled with unconstrained token-creation permissions (iam.serviceAccounts.getAccessToken or equivalent). Furthermore, UNC6993's JSON session-token theft highlights why MFA alone is not a silver bullet if session tokens aren't bound to device posture or continuous authentication checks at the Policy Enforcement Point (PEP).
Exam Mindset Callout (Think Like a Manager)
On the CISSP exam, when faced with service account compromise, look beyond tactical key rotation. The primary failure is a lack of Least Privilege and Identity Governance over non-human accounts. Always prioritize eliminating static long-lived service account keys in favor of short-lived workload identity federation, enforcing strict RBAC/ABAC boundaries, and requiring Separation of Duties before provisioning high-cost cloud APIs.
CCSP Domain 5: Cloud Security Operations (17%) & CISSP Domain 7: Security Operations (13%)
Domain Mapping
Continuous monitoring, UEBA (User and Entity Behavior Analytics), billing/consumption anomaly detection, baseline configuration, and drift detection.
Real-World Connection
A $100,000 single-day cloud charge doesn't happen silently—it generates massive API telemetry spikes, regional resource enumeration, and abnormal service account creation ("burn and rotate"). Disguising a rogue account as a "billing optimization utility" preys on organizations that rely on manual log review rather than automated behavioral baselines.
Exam Mindset Callout (Think Like a Cloud Architect)
Under the CCSP Shared Responsibility Model, the Cloud Service Provider (CSP) guarantees the availability and underlying infrastructure of the foundation model API, but the Cloud Service Customer (CSC) is 100% responsible for securing API keys, IAM roles, quota limits, and consumption monitoring. If an exam scenario asks how to mitigate resource hijacking (FinOps/Denial of Wallet), pair hard API quota caps (preventative technical control) with automated SIEM/SOAR billing and token-velocity alerts (detective/automated response control).
CISSP Domain 8: Software Development Security (10%) & CCSP Domain 4: Cloud Application Security (16%)
Domain Mapping
API security gateways, middleware vulnerability management (CVE-2026-40217), shadow AI, and securing local developer environments/CLIs.
Real-World Connection
The reconfiguration of legitimate Claude Code and OpenAI Codex CLIs via vibe.aiok[.]me demonstrates how developer convenience and Shadow AI bypass enterprise controls. By setting local CLI configs to danger-full-access and routing traffic through unauthorized third-party relays, employees inadvertently expose proprietary source code to man-in-the-middle inspection while removing local host sandboxing.
Exam Mindset Callout (Think Like a Manager)
When employees use unauthorized resellers to access AI coding assistants, technical blocking is only half the answer. The ISC2 mindset points first to Acceptable Use Policies (AUP), AI Governance frameworks, and Supply Chain Risk Management (SCRM)—providing sanctioned, governed enterprise AI tooling so developers aren't incentivized to run untrusted setup scripts from lookalike domains.
Actionable Practitioner Takeaways: Hardening Your Environment
To keep your organization from funding the next underground LLM Mixer, implement these controls across your cloud and developer estates immediately:
Enforce Hard Quotas and Budget Circuit Breakers
Do not rely purely on billing threshold emails. Configure automated cloud budget circuit breakers and strict per-key/per-region rate limits (RPM/TPM) on AWS Bedrock, Google Vertex AI, and Azure OpenAI endpoints so a compromised token cannot scale to $100,000/day.
Eliminate Static Service Account Keys
Audit all cloud IAM Service Accounts with access to AI/ML APIs. Replace static JSON keys and long-lived PATs with Workload Identity Federation and short-lived OIDC tokens, and strip unnecessary token-creation (impersonate / getAccessToken) permissions.
Patch AI Routing Middleware Immediately
If you run self-hosted LLM gateways or proxy middleware like LiteLLM, patch CVE-2026-40217 and isolate management interfaces behind Zero Trust network access (ZTNA) rather than exposing them to container clusters or the public internet.
Hunt for Rogue "Billing" Service Accounts & CLITampering
Query cloud audit logs for rapid "burn and rotate" service account creation/deletion patterns and inspect newly created accounts masquerading as billing or optimization utilities.
Use EDR/MDM to monitor developer endpoints for unauthorized modifications to~/.codex/config.tomland~/.claude/settings.json(specifically hunting fordanger-full-accessflags or outbound connections to untrusted relay domains likevibe.aiok[.]me).
Deploy Secret Scanning in CI/CD
Enforce pre-commit hooks and continuous repository secret scanning across GitHub/GitLab to revoke leaked LLM API keys before automated scraper bots harvest them.
Did you enjoy CarlsCloud.com™ today and did I help you at all?
If so, buy me a coffee or just shoot me a note via LinkedIn to say thanks it would mean a lot! -Carl